/ apr 2026 · tokyo
The Autonomous SOC: AI-Driven Supply Chain Security & SBOM Remediation
DevOpsDays Tokyo
/ abstract
In modern cloud native delivery, the speed of shipping outpaces the speed of security.
Vulnerability scanners produce thousands of CVEs against every release; engineering teams ignore most of them; and the ones that actually matter slip through.
The fundamental problem is not detection, it is decision and remediation at machine speed.
In this session, Himanshu walks through how to build a reachability-aware autonomous Security Operations Center directly into Kubernetes-native CI/CD pipelines. AI agents consume SBOMs and CVE feeds generated with Trivy, score vulnerabilities through reachability analysis (does this CVE actually touch a live code path?), and propose patches as policy-gated pull requests via Kyverno, OPA, and Argo CD. Falco and Tetragon provide runtime signals back to the agent loop, closing the cycle from runtime evidence to source-tree fix.
The talk covers the closed-loop architecture, the failure modes real teams hit.
/ from linkedin · 1 may 2026
open note →DevOpsDays Tokyo was everything ''
I gave a session on Autonomous SOC: AI-Driven Supply Chain Security & SBOM Remediation
Been exploring Japan in between and just absorbing it all
Huge love to the phenomenal speakers- Nathen Harvey, Andrew Clay Shafer, Edwin Alan Moedano Cardiel, Weithenn Wang, riccardo soro , Nicolas Fantoni, Augustin Lu, Ludovic TOISON , Dr. Joe Perez + folks that I missed
Thanks to Alex Papadimoulis , Sasa-san~~ , Emi-san~~, organising team and translators for holding the whole thing together.
Maybe already plotting a Taiwan trip soon to reunite with Augustin, Weithenn, Rose and the crew there '
Sushi time was fun :) Akihiro Okuda, Hugo Marin
'
On the talk side:
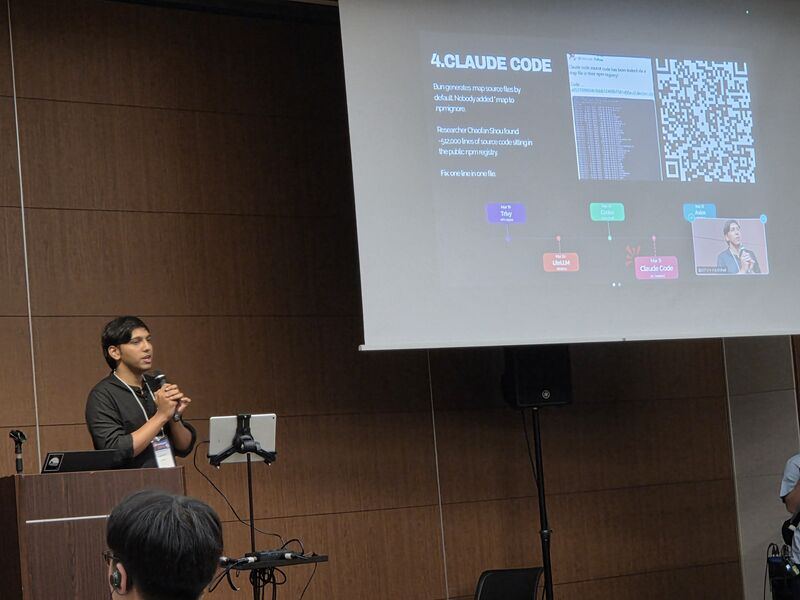
Over the last few weeks- Trivy, LiteLLM, Axios, OpenAI Codex, Claude Code, Railway CDN, Vercel, pretty much every major tool in the modern stack had a supply chain incident.
Things we use personally and at enterprise scale.
So I built something: a plug-and-play autonomous SOC you can drop straight into your GitHub Actions pipeline.
Open source, and I'll keep iterating, contributions very welcome.
Slides link: lnkd.in/dB_kHz2M
GitHub repo link: lnkd.in/dXQwMhQu
More updates soon :)
/ from linkedin · 10 apr 2026
open note →A lot of crazy things happened last week
Was busy building and lazy enough to make seperate posts so dumping all into one here +_+
- -AWS Student Community day was successfully hosted by AWS Cloud Club PICT on 4th April. As a founder of this club, always wanted to host a SCD and thanks to my juniors for organising
I was in the organising and the panel discussion
Btw, AWS Cloud Club PICT has grown to the largest AWS club worldwide with 5k+ members :)
'
- -Thanks to Bhoomi Raut and AWS Cloud Club at Sanjivani College of Engineering for inviting me as a speaker at AWS Student community Day Sanjivani.
I talked about AWS Lambda Durable functions along with step fns and eventbridge onto how to create stateful applications
The students were eager to learn with more than 500+ attendees!!
'
- -Thanks Omanand Swami for inviting me for the inauguration of AWS Cloud Club at JSPM RSCOE on 7th April
I talked about some cloud fundamentals
'
- -Thanks Ram Iyengar for scheduling an OpenSSF live event on 9th April where I talked about Autonomous SOC
Def troubled him a lot in organising it smoothly
'
- -And a small mention onto the inaguaration invite to I2IT some weeks back. Was nice to see Faizan and some I2IT folks at AWS SCD Pune
And finally a talk at DevOpsDays Tokyo coming up soon.
There's some interesting updates coming up too. Currently just focusing on as much as I can focus on building.
That said, IM AT HONGKONG''. Anyone from HK up for coffee chats or lock in at some cafe' Hit me up!!
/ from linkedin · 31 mar 2026
open note →Japan, I'm coming!!
Excited to share that I will be speaking at DevOpsDays Tokyo 2026 (Apr 14-16) on the topic- 'The Autonomous SOC: AI-Driven Supply Chain Security and SBOM Remediation'
The timing could not be more relevant. The last two weeks were a supply chain security disaster:
' TeamPCP compromised Trivy (a security scanner) and cascaded through 5 ecosystems in 8 days
' LiteLLM (95M downloads/month) was backdoored via stolen PyPI credentials from the Trivy breach
' Axios (83M downloads/week) was hijacked via a stolen npm token, deploying a cross-platform RAT
' OpenAI Codex had a command injection flaw that turned Git branch names into credential-stealing payloads
' Claude Code's entire source code leaked via a .map file accidentally shipped to npm
Every one of these exploited the same structural flaw: AI and developer tools hold elevated credentials by design, and nobody is monitoring them with SOC-level rigor.
That is exactly what this talk is about. How to build a closed-loop system that catches these before they cascade. I will post some content about this in the upcoming days.
Also going to be in Hong Kong'' and Malaysia'' around the same time. Would love to meet builders and the tech community across all three countries.
Anyone in Japan, Hong Kong, or KL up for coffee chats, meetups, or office tours' Please hit me up!!
Thanks Alex Papadimoulis and the DevOpsDays Tokyo team :)